Short answer: study the technique, choose the app separately
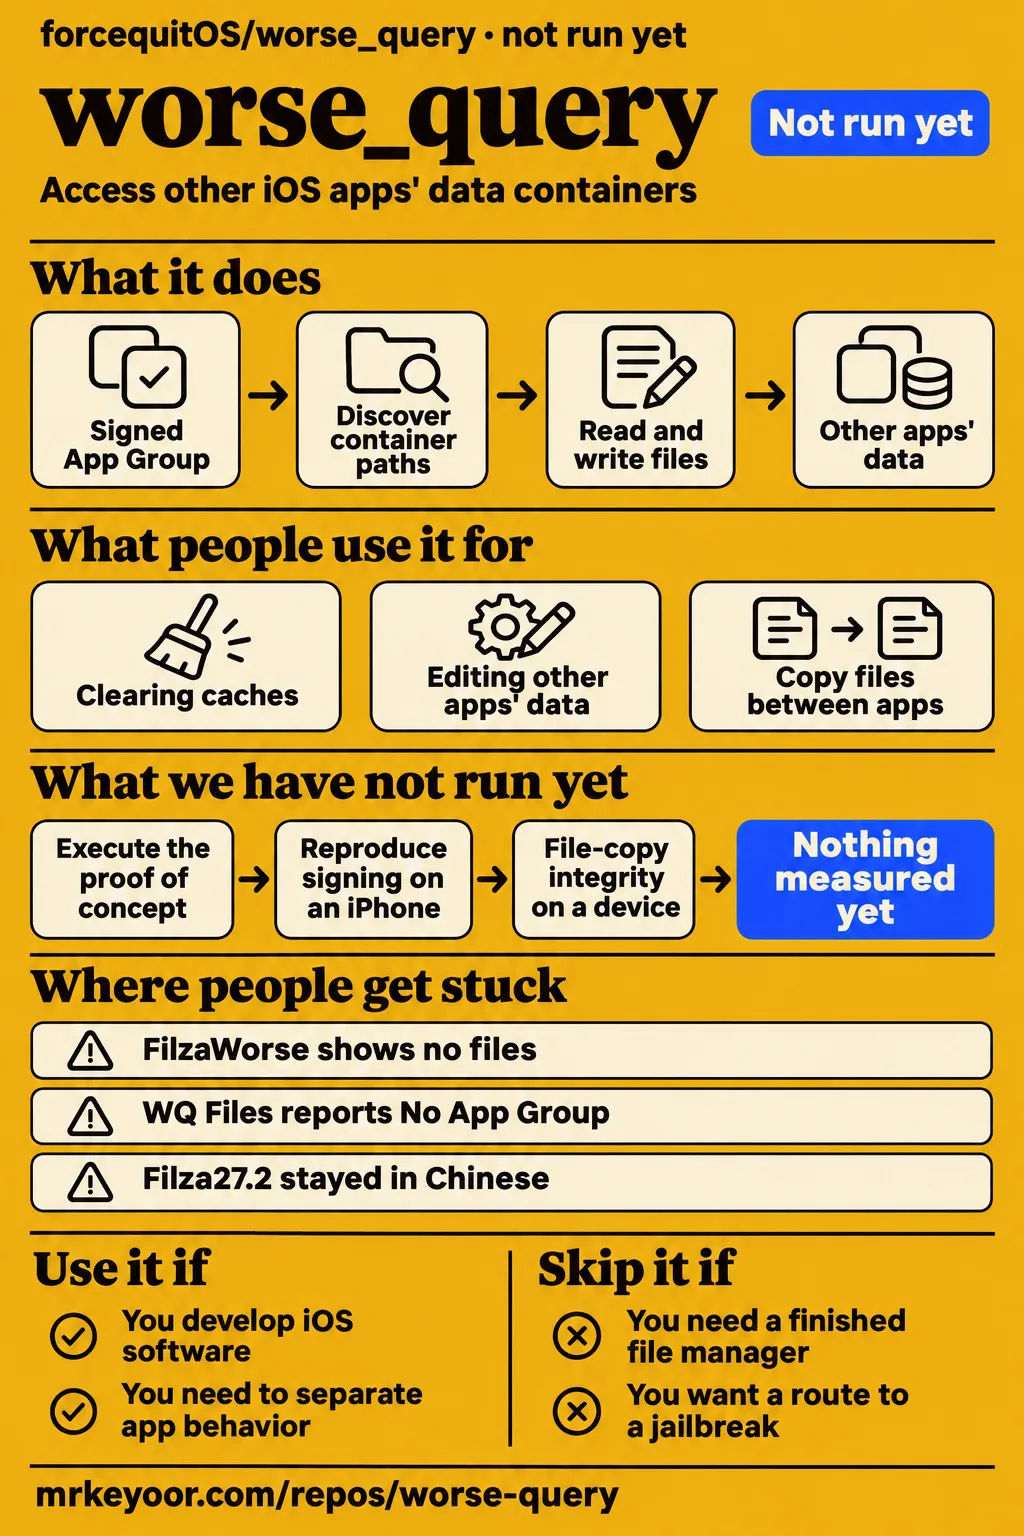
worse_query is a developer proof of concept for crossing iOS app-container boundaries, and its README says it is not useful by itself. Use it if you develop iOS software and want to understand the documented access boundary. Skip it if you want a finished file manager or a route to a jailbreak: the author explicitly rules out both expectations.
Our November 20 assessment stopped before execution because the harness did not support Objective-C and found no Dockerfile. That leaves the recommendation grounded in the project documentation, derivative-app documentation and attributed user experiences. The useful question is whether a particular app gives you the file operation you need, on your particular iOS build, with the signing permissions it requires.
What people use worse_query for
People have used worse_query through cache cleaners and modified file managers, with results ranging from a working local experiment to an app showing no files.
| Person or project | What they did | What came back |
|---|---|---|
| INTRUDX, commenting on r/jailbreak | Cleared caches with WQFiles on an iPhone 12 mini while also discussing a GestaltX tweak | Said the phone felt faster, then questioned whether clearing caches explained it |
| Torrekie, FilzaWorse's author | Patched Filza to use worse_query for limited file modifications | Reported success on their machine and said accessible paths could not be extended |
| Thalha547, in Torrekie's thread | Tried opening files in FilzaWorse | Reported that files were not shown inside the app |
| Christoph Kolbicz's WQ Files, described in reporting | Packaged the technique as a file manager | The video account describes browsing, exporting, editing and deleting other apps' data without a jailbreak |
INTRUDX's exchange is a useful antidote to the cache-cleaner pitch. The first comment praises both WQFiles and another tweak. Later, after another commenter challenges the explanation, INTRUDX asks whether cache clearing caused the improvement. That is a report of perceived responsiveness with competing explanations, not a before-and-after speed test. If speed is your only reason for installing it, this thread gives you no measured gain to expect.
The YouTube explainer about worse_query and wallet exposure describes WQ Files through BleepingComputer's reporting. Its transcript is an explanation of the tool, not a recorded file-management benchmark by the presenter. The distinction matters when a video sounds like a demonstration but actually retells someone else's account.
What happened when we ran it
We did not run worse_query at commit d1540e2 on November 20, 2026: our 3-CPU, 8 GB sandbox had no supported Objective-C execution path, and the repository had no Dockerfile.
| Check | Recorded result | What you can conclude |
|---|---|---|
| Build/test harness | NOT RUN: unsupported ecosystem, Objective-C; no Dockerfile | No installation, build or test result |
| Separate deployment safety step | FAILED because none of the accepted Compose filenames existed | The deployment attempt stopped at its prerequisite |
| Teardown | Reported ok | Cleanup completed, not an application task |
The deployment safety log says unsafe repo: none of compose.yaml, compose.yml, docker-compose.yaml, docker-compose.yml exists (rule: a compose file is required). Here, “unsafe repo” is the harness's label for a missing deployment prerequisite. It is not a finding that the source code is malicious or that the technique fails on an iPhone.
A generic run-summary line says it was deployed with its own Docker Compose, contradicting that failed safety step. The concrete failure and the NOT RUN outcome take precedence. There is no successful app task to describe. The image entry is n/a, which identifies neither an operating-system version nor a runtime version.
Where people get stuck: signing, empty views and limited paths
FilzaWorse's author reported success, but a reader in the same thread reported an empty file view and received no recorded diagnosis.
Thalha547 first asked whether iOS 27.0.1 without a jailbreak was supported. Torrekie answered yes. The reader then asked for usage documentation and later wrote that files were not being shown. The exchange ends without a fix. Neither reinstalling nor changing a signing service can honestly be presented as the solution to that person's problem.
For your own investigation, distinguish these symptoms rather than treating every blank view as the same failure:
| Symptom or requirement | What the documentation or thread says | Useful next step |
|---|---|---|
| FilzaWorse shows no files | Thalha547 reported this without a diagnosis | Preserve the exact app version and symptom when asking its author |
| WQ Files reports No App Group | Its README says the signer must supply an App Group | Read the group shown at the top of Log before changing file operations |
| WQ Files refuses tokens after a cache swap problem | Its README documents automatic repair and Reset Access Cache | Use that documented recovery for that specific error |
| A requested path stays inaccessible | Torrekie says FilzaWorse cannot extend worse_query's supported paths | Compare the target with the upstream path list |
An App Group is a shared storage container assigned to an app through its signed permissions. The worse_query README requires one. WQ Files' current signing instructions explain why choosing an installer matters: they say Sideloadly does not add the group, while AltStore and SideStore create one. A developer profile must preserve the relevant permission. A filename that looks like a valid IPA, the packaged iOS app, tells you nothing about that permission.
English documentation does not guarantee an English derivative
The worse_query README is in English, while the Filza27.2 announcement reports an interface that stayed Chinese instead of following the phone's language.
BowlSuper9915 put the problem directly in the Filza27.2 announcement, and commenters also reported Chinese text. Relative-Muffin-6431 asked what the release did because they could not understand what was happening. For a tool that can delete another app's data, unreadable controls are a practical reason to choose a different interface.
Keep the products separate. WQ Files' current README documents English and a Language setting. That does not repair Filza27.2 or prove anything about its translations. If English controls are essential to you, the documented WQ Files interface is a more useful starting point than assuming every derivative inherits the upstream README's language.
Large file collections turn discovery into the first obstacle
The technical reference describes full-volume inode scanning as a discovery bottleneck and says WQFiles v0.8 introduced LaunchServices database lookup for container paths.
An inode scan searches filesystem identifiers to discover folders whose names the app cannot simply list. The reference contrasts that scan with reading iOS's LaunchServices database, which maps apps to their containers. This is a change in how folders are found, not evidence that reading or editing every file has become faster.
The current WQ Files README preserves that distinction: App Data, App Groups and Extension Data can come from the database, while Internal Daemons still need scanning. If your goal is to reach one app's documents, a broader filesystem scan may be irrelevant work. If you need daemon containers, the discovery path itself deserves attention before you judge the file browser's responsiveness.
Wallet risk comes from reachable secrets, including encrypted copies
Coinspect warns that copying an encrypted seed file can expose it to offline password guessing, so “the seed is encrypted” does not end the security discussion.
Coinspect's November 11 post explains that an attacker holding the file can attempt to crack its password offline, with weak key derivation making that easier. This is a threat model, not a claim that worse_query has cracked a named wallet. Plaintext seeds and password-encrypted seeds create different obstacles for an attacker, but both make the storage design relevant.
The file-access boundary also matters. The technical reference describes System Data access as directory listing only because its contents are root-owned. Seeing a folder name is different from reading its contents. Neither that listing nor the app-container access claim warrants saying that every secret on an iPhone is exposed.
For file editing, the derivative's safeguards are part of the buying decision. WQ Files' README says its SQLite editor works on a copy, checks integrity and checks whether the original changed before saving. It also tells you to force-quit the target app first because WQ Files cannot tell whether it is running. Those are documented guardrails for concurrent data, not permission to edit a live database casually.
worse_query vs bad_query, WQ Files and FilzaEscaped
worse_query replaces bad_query as a developer technique; WQ Files and Filza-style derivatives are the interfaces you would compare for everyday file work.
| Choice | Why you would choose it | Boundary that changes the decision |
|---|---|---|
| worse_query | Study the newer container-access proof of concept | The author requires an App Group and calls it a developer PoC |
| bad_query | Investigate the earlier technique or its historical compatibility | Its README calls it a developer PoC too; worse_query's author says the successor replaces it |
| WQ Files | Use a documented file browser and app-data manager | Its README covers signing, recovery and file operations, with OS-build restrictions |
| FilzaEscaped / FilzaWorse / official Filza | Prefer the Filza experience | Torrekie presents FilzaWorse as a similar experience with limited file modifications, and criticizes official Filza 5.0's interface |
The reference distinguishes bad_query's older traversal approach from worse_query's App Group approach. You should not select bad_query merely to avoid the newer requirement: the technical account says the older traversal was patched in iOS 27.2. Pick by the actual technique and supported build, rather than the similarity of the names.
Torrekie's preference for an older Filza experience is a personal interface judgment. The same announcement says FilzaWorse directly modifies original Filza binaries and could not be fully open-sourced. If inspecting all of the application code is a requirement for you, that distribution model deserves attention independently of worse_query's open-source code.
What the other reviews get wrong
DigitBin's claim of one public derivative is contradicted by the Filza announcements, and older patch accounts need to be read with their dates attached.
DigitBin describes WQ Files as the one public tool built on the technique. Torrekie's FilzaWorse announcement and BowlSuper9915's Filza27.2 thread make that exclusivity claim untenable. This is not a reason to treat all three apps as equally capable.
MaxwellCTI says manually sideloaded or enterprise-provisioned IPAs are required. NodeWitness's November 10 article says nobody involved had confirmed an App Store route. The November 12 iOS-TR report attributes that possibility to forcequit, conditional on a malicious app passing review. That updates the attribution; it does not identify an actual malicious App Store app.
The Crypto Guide's November 10 account says there is no confirmed fix. On November 17, BitDATAExchange reported a fix in iOS 27.3 beta 2; RZ7Vc made the same patch claim the next day. The current WQ Files README now also says that build blocks access. The chronology has advanced beyond those earlier “unpatched” headlines, while official patch confirmation and our reproduction are separate questions.
Two video claims also need narrowing. The transcript of video s0XkwYSsUd0 names iOS 16 and 17, conflicting with the project's iOS 26 and 27 description. The 9-UxnZIPo_0 transcript says an installed app can read everything, whereas the technical reference and Torrekie describe restricted paths.
Finally, NodeWitness says its stated README range contains all three Binance-listed versions. A range written as iOS 26.0–26.7.2 plus 27.2 does not explicitly include 27.0.1. Broader compatibility claims need their own attribution, as the FAQ below provides.
Questions people ask
Banking-app and crypto-wallet files can be at risk when they contain reachable secrets; the warnings describe possible exposure, not proof that every account can be taken over.
Are banking apps and crypto wallets at risk from worse_query?
The risk depends on what each app stores in accessible files. Quan_Chain's account of Binance's warning identifies seed phrases, private keys and login credentials as possible exposures. Coinspect adds the offline-guessing risk for copied encrypted seed files. Neither statement is a test of a named banking app's authentication or a blanket claim that its server-side checks are bypassed.
Which iOS versions are affected by worse_query?
The upstream README lists iOS 26.0–26.7.2 and 27.2. NodeWitness quotes forcequit saying 27.2.1 and 27.3 beta 1 were still affected. WQ Files' current maintainer documentation says access stops at 27.3 beta 2. Read these as separate statements with different scopes, rather than one continuously tested version matrix.
Can worse_query read and write another app's files or copy files between apps?
The technical reference describes read/write access to user-app data containers, and WQ Files documents Copy to Folder and Move across apps. Those operations belong to the derivative's interface. The proof of concept alone is not a copy-and-paste file manager, and directory listing in System Data carries a different access boundary.
Does WQFiles work with LiveContainer?
The current WQ Files README documents a LiveContainer-specific adjustment: it uses the real App Group folder instead of the stand-in folder reported inside LiveContainer. That is a maintainer-documented compatibility path. Specialist_Tax9686's November 19 Reddit question has no answer in its thread, so that conversation contributes a question rather than a successful user result.
Where can I find instructions for using FilzaWorse?
Start with Torrekie's announcement, which describes the modified app and its path restrictions. Thalha547 asked for a how-to in that thread, but the conversation contains no returned instructions. WQ Files' signing and recovery documentation describes a different app and should not be substituted as a FilzaWorse manual.
What does the worse_query-based Filza release actually do?
Torrekie describes FilzaWorse as patched Filza for limited file modifications using worse_query. The separate Filza27.2 thread includes a yes reply to a read/write and cross-app-copy question, alongside language complaints. That brief reply supplies less detail than the author's explicit path restriction, so universal filesystem access would be an overstatement.
Can worse_query be combined with another exploit to make a userland jailbreak with SpringBoard tweaks?
There is no demonstrated combination in Sasobhabha's X discussion: it contains a proposal and a speculative reply. The upstream author says worse_query is not relevant to a jailbreak. A question mentioning another exploit does not document a working chain or SpringBoard tweak support.
Does a userland sandbox escape provide enough access for a jailbreak?
For worse_query, the author explicitly says no jailbreak relevance, and the technical reference describes container access with filesystem-permission limits. Userland means the ordinary software environment outside the kernel, the operating system's core. Access to another app's files alone is not evidence of control over that core or of the privileges a particular jailbreak requires.
Can someone steal crypto through worse_query just by sending a link?
The YouTube explainer states that the code must be in an app already installed on the phone. A link alone is not the attack described there. A separate delivery or execution exploit would need its own evidence and should not be silently added to worse_query's capabilities.
Does worse_query affect hardware wallets?
A hardware wallet's signing keys kept off the iPhone are outside the app-file exposure described by NodeWitness. Copies of recovery material saved in phone files create a separate exposure. The relevant distinction is where the secret resides, rather than whether the companion app displays a hardware-wallet brand.
Is worse_query a Binance-specific problem?
No. NodeWitness quotes Binance describing an iOS-level issue, not one unique to the exchange. The repository's app-container path list also describes a platform boundary. An exchange warning identifies why financial users should care; it does not narrow the technique to that exchange's application.
Why did the researcher publish worse_query?
The YouTube explainer says it does not know what contact occurred with Apple before publication. The README identifies a developer proof of concept. Those facts do not establish the researcher's motive or justify retelling a disclosure dispute as settled history.
What we have not tested yet
Our lab did not execute the proof of concept, reproduce signing or issue a sandbox token on an iPhone. The stopped harness attempt supplies no install duration, build result, passing-test count, runtime version or security audit.
We have not tested WQ Files, FilzaWorse or Filza27.2 on a device, including their language settings, LiveContainer behavior, recovery operations, file-copy integrity or concurrent database writes. The current WQ Files README adds explanations beyond the older user threads; it does not retrospectively diagnose Thalha547's empty view or establish a corrected Filza27.2 translation.
No measured cache-cleaning speed gain, sustained large-library workload, named-wallet extraction or cryptocurrency theft is established by our work. Official confirmation of the reported beta fix and a controlled comparison of access before and after that build are also outside this review. The next useful lab result is a harmless file read in a disposable app container on each side of the reported patch boundary, with the signing permissions and OS build recorded.