A dashboard for personal usage, with accuracy to check
TokenTracker puts usage from several AI coding tools in one place. The decision is whether its dashboard and desktop views help you understand your own activity, and whether the integrations you use agree closely enough with provider records.
The supplied current README advertises 46 supported tools. At our measured commit, daa6c55, the README advertised 42. Neither number measures our integration coverage. Upstream documents hooks, plugins, local SQLite databases, session logs, and some provider API requests as collection methods.
The documented interface includes a browser dashboard, native apps for macOS, Windows, and Linux, four desktop widgets, a pixel pet, and 15 achievement tracks. tokentracker status --json supplies machine-readable status. Usage is documented as aggregated into 30-minute UTC buckets in local SQLite. We did not exercise these interfaces or measure a coding workload.
What our recorded run establishes
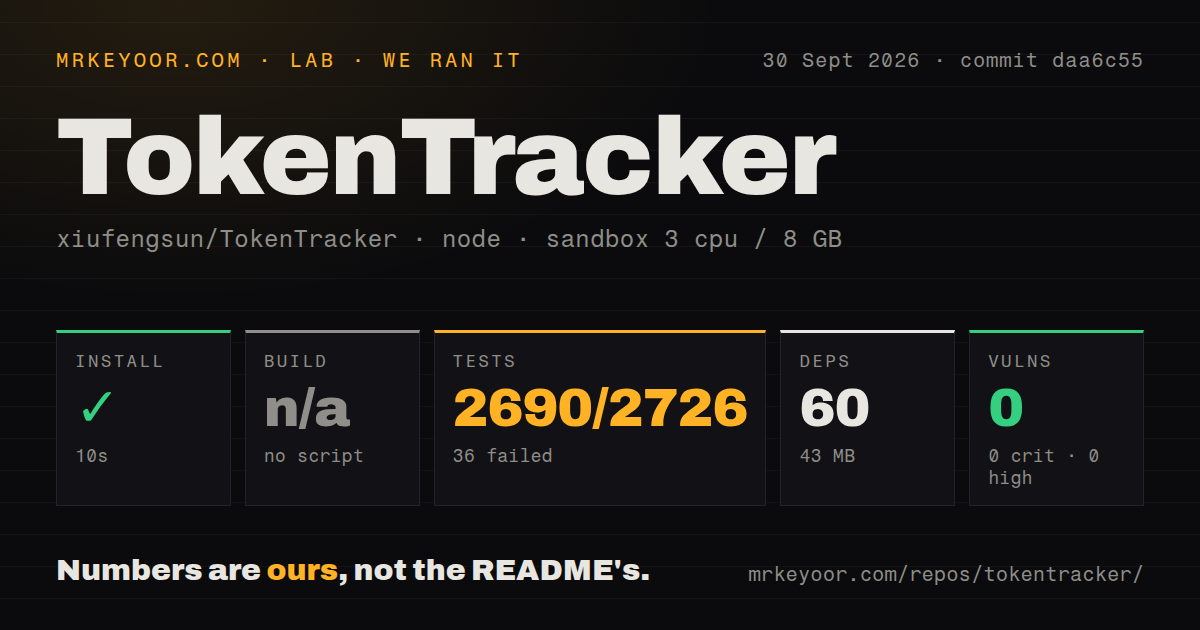
Our stored run began on 2026-09-30 at 12:10:19.187 UTC using commit daa6c55099d34458ff773f6c1edd777f16fb7693. Its recorded configuration was 3 CPUs, 8 GB of memory, and image lab-node:22. The actual install output identifies Node v20.20.2 and npm 10.8.2; the image label does not establish the runtime version.
The dependency-install step exited 0 after 10.153 seconds. The summary records 60 dependencies and 43 MB, but the retained command output says 48 packages were added in 4 seconds. We cannot explain that difference from the retained record. Successful dependency setup does not establish that a packaged CLI was installed, hooks worked, or the dashboard launched.
The output also contains an engine warning: undici@8.10.2 requires Node >=22.19.0. It reports prebuild-install@7.1.3 as deprecated. These warnings qualify the successful exit; they do not establish a runtime failure or explain the test failures.
The recorded npm audit advisory total was zero across critical, high, moderate, and low severities. Coverage is unknown. This result does not establish that TokenTracker is safe, that all dependencies were assessed, or that desktop artifacts were examined.
The harness skipped its build step with reason "no script". The repository nevertheless records a dashboard:build script and platform build scripts. The commit README also documents building the dashboard. No build was verified in our run.
The test command exited 1 after 77.748 seconds, rounded to 78 seconds in the summary. Its retained node:test footer reports 2,759 tests: 2,690 passed, 36 failed, and 33 skipped. The stored parser total of 2,726 is the sum of passes and failures, excluding skips. These are recorded summary counts, not independently reconciled exhaustive unique coverage. Skipped tests were not failures.
The retained tail names test/zed-parser.test.js as a failing test file and includes generic test-failure messages. It does not establish every failure's cause. A failed command at this historical commit cannot establish that the current product is broken.
For context, the stored checkout metrics were 1,343 files, approximately 312,411 source lines, and 29.6 MB, with 11 CI workflow files, a tests directory, and no Dockerfile or Compose file. Those measurements describe repository shape, not product reliability.
Setup changes local configuration and can make network requests
The README requires Node.js 20+ and documents npx tokentracker-cli as the quick start. Upstream says first run installs managed hooks, syncs records, and opens the dashboard at localhost:7680. The measured-commit troubleshooting section documents automatic port fallback and a default of 7681 under WSL. These are documented behaviors, not launch results from our run.
Use tokentracker status to inspect integration state and doctor for the documented health check. The documented tokentracker uninstall command removes managed hooks and local TokenTracker configuration and data. Passive readers inspect files the coding tools already create; hook and plugin integrations can change those tools' configuration.
Local processing does not imply offline operation. The current README lists provider quota checks using existing credentials, update checks, GitHub star counts, pricing refreshes, a daily heartbeat, and PostHog page views. It also lists optional Sentry error reports when a DSN is configured. TOKENTRACKER_NO_TELEMETRY=1 or DO_NOT_TRACK=1 disables anonymous telemetry according to upstream; those settings do not disable every documented network request.
The README says prompts, responses, and code are not saved or uploaded by the tracking path. We did not audit that implementation or capture network traffic. Treat it as an upstream privacy statement.
Cloud sync and leaderboard participation are optional. The current README distinguishes free local features from the officially hosted TokenTracker Cloud service, which it lists at USD 4.99 per month or USD 39.99 per year before checkout tax. It describes the complete self-hosted installation as a technical preview. Those current terms should not be inferred from the historical dependency run.
Cost estimates need provider-level reconciliation
Upstream explicitly describes Grok cost as estimated because local telemetry lacks a stable prompt, output, and cache split. It also says models without published pricing can show $0. For Devin models without pricing data, the README explicitly warns that a $0 figure does not mean free usage. A dashboard dollar total therefore needs context before it becomes a financial record.
The OmO report concerns TokenTracker v1.1.3, with the reporter first noticing the behavior on v1.1.0. It describes Anthropic-subscription requests appearing in both OmO and Claude records. On October 1, the maintainer acknowledged the reader's overlap limitation and said there was no shipped fix yet. The supplied issue history subsequently records closure as completed through PR #788 on October 13, referencing commit 10f0a23. That is evidence of a linked fix, not our verification of a released binary or every overlap case.
The supplied Kiro report concerns embedded CLI v1.0.7 and is also marked closed. Its discussion documents an undercounting estimator and uncertainty about reconstructing request input from context percentages. The supplied extract does not establish the closing change or a verified replacement estimator. We cannot describe that historical report as an open current defect or claim that current Kiro totals are exact.
Neither report came from our sandbox test command. We did not compare TokenTracker totals with invoices, subscription credits, or provider usage exports. Before using the totals for reimbursement or chargebacks, reconcile the relevant integration with authoritative records.
Desktop packaging needs a separate check
The README directs Debian 12 users to the roughly 120 MB AppImage because the .deb depends on libappindicator3-1, which Bookworm does not provide under that name. GNOME requires an AppIndicator extension for the tray. Windows and WSL scanning has provider-specific limits, so check the documented scan mode for your tools.
At the measured commit, the README described the macOS app as ad-hoc signed and not notarized with an Apple Developer ID, with an Open Anyway procedure for Gatekeeper. That historical documentation does not establish the signing state of a current download.
Issue 720 reports Kaspersky behavior detection and quarantine of tracker.js in v1.1.2 on Windows. The reporter also said TokenTracker.exe was unsigned. Matching a file hash to upstream does not settle a behavior alert or establish either malware or a false positive.
On October 14, the maintainer reported submitting the v1.3.14 Windows installer for Kaspersky reanalysis and said the reported tracker.js hash was shown as Clean on OpenTip. The issue remained open for tracking on October 24. That update does not establish that every installer or behavior alert has been cleared. We did not perform antivirus or signing checks.
The historical v1.1.3 release separately documents Command Code tracking, a Windows desktop quota widget, Linux sign-in fixes, and SHA-256 checksums for six desktop artifacts. Checksums identify artifacts; they do not establish compatibility or safety.
Choosing an interface and a next step
ccusage documents daily, weekly, monthly, and session reports from local coding-agent data, including combined reports across detected sources and JSON output. It is a relevant choice when those terminal reports answer your question.
Tokscale documents an interactive TUI, CLI reporting, web visualization, JSON export, and optional leaderboard submission. Consider it when terminal exploration is your preferred interface. We did not benchmark either alternative against TokenTracker.
TokenTracker's documented dashboard, desktop views, and quota display make it a candidate for personal monitoring. Evaluate the integrations you use, check their permissions and network behavior, and compare a defined period with provider records. Our stored run supplies dependency and test-command evidence, not an end-to-end adoption result.
How the scores work
These are editorial evidence ratings, not benchmark results. The scale is 1 for major documented obstacles, 2 for limited support with important unresolved checks, 3 for a usable documented path with material verification gaps, 4 for detailed support with narrower gaps, and 5 for strong documentation plus direct verification of the relevant behavior. Setup covers reaching a working application; docs covers actionable instructions and caveats; community covers visible maintenance and issue handling; maturity covers verified reliability and compatibility. Unknown adoption and untested platforms do not earn higher scores.