mrkeyoor.com_
Sat 07 Nov 01:58 UTC
Dev Toolsevaluationupdated 07 Nov 2026

blackbird review

Blackbird is a command-line OSINT tool for searching for accounts by username or email address. Its README describes WhatsMyName integration, report exports and optional AI profiling. Search results are leads to verify; our sandbox did not assess whether matches identify a particular person.

Verdict

Blackbird completed our recorded installation, build and test steps, but pip-audit reported 167 known vulnerabilities in the measured environment. Defer routine adoption until the advisory details have been reviewed. A contained evaluation can assess the username and email workflow, with matches and misses checked against known accounts.

We ran it

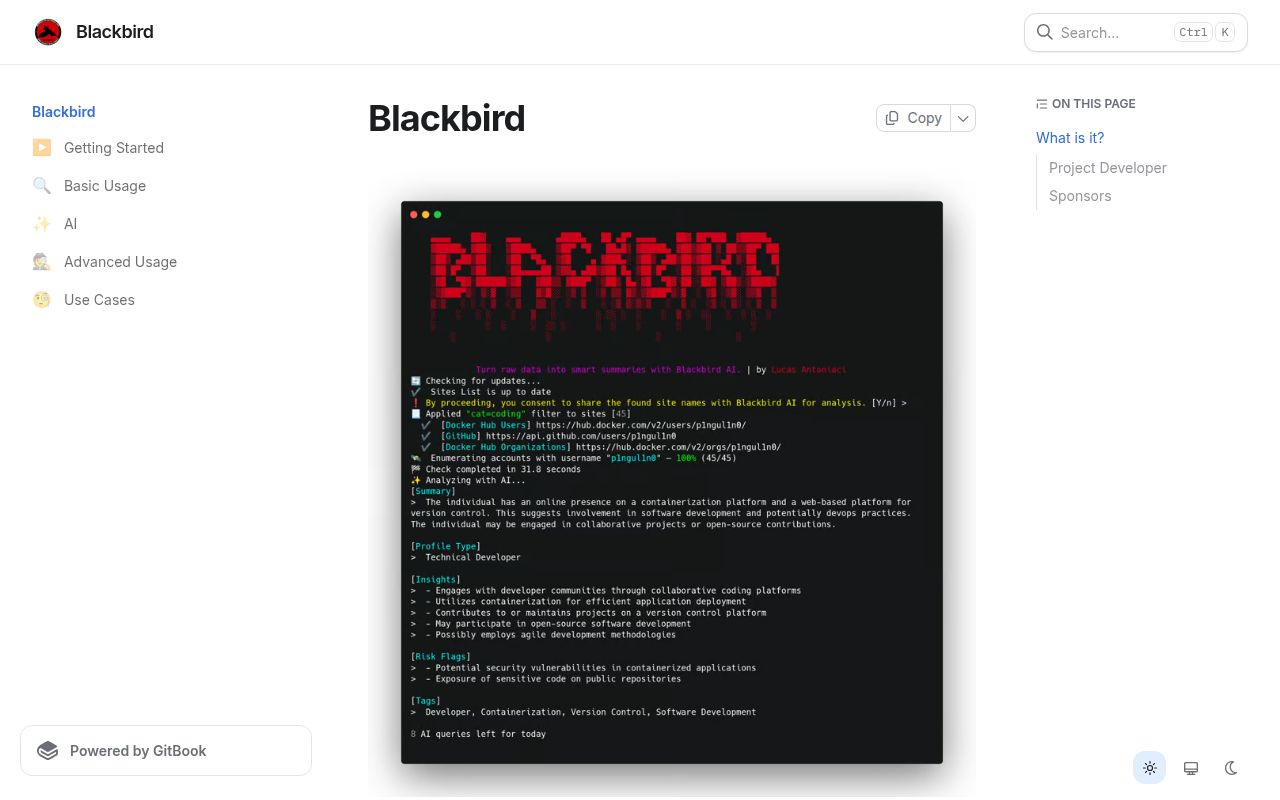
Lab card: what happened when we ran blackbirdScreenshot of blackbird (p1ngul1n0.gitbook.io/blackbird)
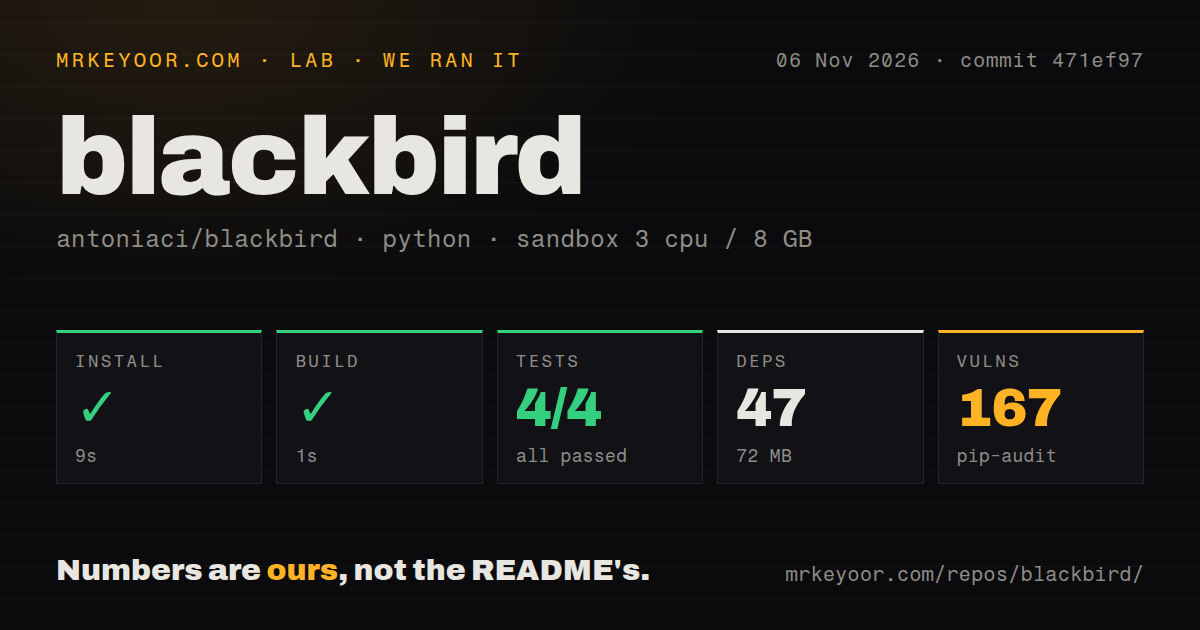
Install✓ · 9s47 packages · 72 MB
Build✓ · 1s
Tests✓ · 6s4 passed · 0 failed of 4 (pytest)
Known vulns167(pip-audit)
Repo69 files~2,287 lines of source · 2.4 MB · 2 CI workflows · Dockerfile · tests dir

Answers from our run

Does blackbird build from source?

Dependencies installed in 9 seconds (47 packages), and the build succeeded in 1 seconds. We cloned commit 471ef97 into a clean Debian container with 3 CPUs and no project-specific setup.

Do blackbird's tests pass?

Yes. The project's own test command finished in 6 seconds and reported 4 passed, 0 failed (pytest).

Does blackbird have known vulnerabilities in its dependencies?

pip-audit flagged 167 known advisories in the dependency tree at the time of our run.

Who should not use blackbird?

Teams requiring a reviewed dependency audit before adoption: our measured environment reported 167 known vulnerabilities.

What are the alternatives to blackbird?

Sherlock, Maigret. Blackbird completed our recorded installation, build and test steps, but pip-audit reported 167 known vulnerabilities in the measured environment.

SetupN/AInstallation and build succeeded in the recorded sandbox, but those results do not establish the difficulty of completing an investigation. Live searches, report output and optional AI setup were not assessed, so setup ease remains unscored.
Docs3/5Documentation receives 3/5 on the public rubric: 1 means orientation only, 3 means an actionable main path with gaps, and 5 means verified coverage across documented paths. The README supplies basic search and AI commands, but its PDF email example omits the email value and its clone example uses a different repository owner. We did not execute these examples or assess the linked documentation.
CommunityN/AThe supplied issue and pull-request extracts show a reported compatibility problem and a merged response. They do not establish sustained support capacity, typical response times or support quality across users, so community remains unscored.
MaturityN/AThe recorded checks passed and the dependency audit reported findings requiring review. Neither result establishes live search accuracy or operational reliability. Without evaluated searches, reports and advisory details, maturity remains unscored.

Who it’s for

Investigators conducting authorized searches who will inspect matching profiles themselves.
Python users evaluating username and email discovery in a contained environment.
Maintainers prepared to review the recorded dependency advisories before routine use.

Who it’s NOT for

Teams requiring a reviewed dependency audit before adoption: our measured environment reported 167 known vulnerabilities.
Investigators who require validated search accuracy: our sandbox did not assess live matches or misses.
Users requiring entirely local AI profiling: the README says site names are sent to an AI engine and documents API-key setup.

Setup reality

Our November 6, 2026 sandbox run at commit 471ef97 completed installation in 9 seconds and the build in 1 second. The test step completed in 6 seconds, with pytest reporting four passed and zero failed. The install recorded 47 dependencies and 72 MB on disk. Pip-audit reported 167 known vulnerabilities. The measurement JSON records eight vulnerable packages, but the supplied evidence does not identify those packages, the advisories or their severity.

The README documents installation with pip install -r requirements.txt and separate username and email commands. These are documentation examples, not live searches we executed. Optional AI has a documented API-key setup step and daily usage limit. The clone example uses p1ngul1n0/blackbird, while the repository reviewed here is antoniaci/blackbird. Keep the repository identity and selected commit with evaluation results.

The configured sandbox had 3 CPUs, 8 GB RAM and image label ghcr.io/astral-sh/uv:python3.12-bookworm. That label does not establish actual runtime or operating-system versions. We did not verify live searches, AI results or exported reports. The supplied record does not establish the latest release status.

The dependency audit changes the adoption decision

Blackbird completed our recorded setup checks, but pip-audit reported 167 known vulnerabilities. Review those findings before adopting the measured environment for routine investigations. Successful installation does not establish whether its dependencies are suitable for a machine holding sensitive research.

Blackbird is a command-line OSINT tool for searching for accounts by username or email address. Its README describes WhatsMyName integration, report exports and optional AI profiling. These are documented capabilities; our sandbox did not evaluate their results. Treat discovered accounts as leads to inspect, rather than proof that a particular person owns them.

What happened when we ran it

Our November 6, 2026 sandbox run used commit 471ef97. Installation completed in 9 seconds, the build in 1 second and the test step in 6 seconds. Pytest reported four passed and zero failed. The sandbox had 3 CPUs and 8 GB RAM configured. Its image label was ghcr.io/astral-sh/uv:python3.12-bookworm, which does not establish the actual runtime or operating-system version.

The recorded install contained 47 dependencies and occupied 72 MB on disk. The checkout was 2.4 MB, with 69 files and approximately 2,287 source lines. The scan found two CI workflow files, a Dockerfile and a tests directory. These measurements describe one checkout and its recorded checks. They do not measure account-search speed or accuracy.

Pip-audit reported 167 known vulnerabilities. The measurement JSON records eight vulnerable packages, but the supplied evidence contains no package names, advisory identifiers or severity breakdown. It does not establish which findings are reachable through Blackbird or which dependency changes would resolve them. The audit count is a reason to investigate, not evidence that Blackbird has 167 exploitable defects.

No live username or email search, false-positive study, AI-output evaluation or exported-report inspection accompanies the lab record. The README's speed and low-false-positive claims remain upstream claims that we have not reproduced.

Basic search and AI profiling need separate evaluation

The README documents cloning the repository, installing requirements and running separate username or email commands. Its clone example uses p1ngul1n0/blackbird, while this review concerns antoniaci/blackbird. Keep the actual repository identity and selected commit with your results.

The README also contains a PDF email example with the email value missing. That command needs an email argument before it is useful as a search example. We did not execute the documented search, export or AI commands, so they should not be read as validated workflows.

Optional AI has a documented API-key setup step and a daily usage limit. The README says only site names are sent to its AI engine. This is the project's description of the feature, not a traffic observation from our sandbox. If profiling must remain entirely local, this documented arrangement does not meet that requirement.

A list of services associated with a handle does not establish someone's occupation, motives or behavior. Check any generated profile against independent evidence. We did not assess the AI's accuracy or inspect its processing of inputs.

A reported compatibility problem has a merged repair

Issue 215 reported missing support for post_body and strip_bad_char in the username checker. The report describes requests that could miss existing accounts because the checker used the wrong request method or failed to remove specified characters from a username.

Pull request 217 says sites with post_body now use POST requests with their headers, and strip_bad_char characters are removed before the URL is built. The supplied page records merge commit 471ef97 on November 3, 2026, matching the commit in our sandbox record. This supports describing a merged repair at the measured revision. It does not establish that our four tests exercised those cases, and we did not reproduce the reported misses or validate the repair with live searches.

The repository metadata records a last push on November 3, 2026. That and the issue discussion show recent maintenance, without establishing typical response times or sustained support capacity. The supplied record does not establish the latest release status.

Choose alternatives by the output you need

Sherlock documents username account searches and individual text files for the usernames searched. Its README also lists CSV and spreadsheet output. Consider it when account links by username cover your task. We have no comparative evidence that it is faster or more accurate than Blackbird.

Maigret describes gathering information from profile pages into a dossier based on a username. Consider it when page information belongs in the investigation alongside account discovery. Neither alternative was audited or benchmarked in this review; each needs its own dependency and result checks.

Documentation rating and next step

Documentation receives 3/5 on an editorial rubric where 1 means orientation only, 3 means an actionable main path with gaps, and 5 means verified coverage across documented paths. The README supplies basic search and AI commands, but the incomplete PDF email example and different clone owner leave gaps. We did not execute those examples or assess the linked documentation. Setup ease, community and maturity remain unscored because the supplied evidence does not establish them.

For a contained evaluation, use known accounts you have permission to check and inspect both matches and misses. Keep commit 471ef97, or the different revision you select, with the output. Before routine adoption of the measured environment, obtain the advisory details behind the 167 findings and decide which dependency changes are required.

Alternatives

ProjectWhat it isPick it when
Sherlock gh↗A username account-search CLI with documented per-username text output.Choose it when username discovery and a list of account links cover your task. Its README also documents CSV and spreadsheet output; we did not test those paths.
Maigret gh↗A username-search tool whose README describes gathering profile-page information into a dossier.Choose it when you want to evaluate page-information collection alongside account discovery. We did not benchmark or audit it.

What people are saying

  1. [github-trending] antoniaci/blackbird

Sources

  1. Blackbird README
  2. WhatsMyName compatibility report
  3. WhatsMyName repair and measured merge-commit proof
  4. Blackbird repository facts
  5. Sherlock README
  6. Maigret README

More dev tools reviews

czkawka · controller-runtime · openchoreo · terraform-provider-azurerm · figma-console-mcp · gg-framework · the whole board →